Practical DevSecOps: Hardening the Supply Chain in the Age of SBOMs
GitHub Actions pipeline: Syft SBOM, Grype gate, keyless signing and attestation with Cosign v3, and admission-time verification with Kyverno.
6 posts with this tag
GitHub Actions pipeline: Syft SBOM, Grype gate, keyless signing and attestation with Cosign v3, and admission-time verification with Kyverno.
An ML pipeline with validated, DVC-versioned data, a safetensors model signed with Sigstore, and least-privilege serving on Kubernetes.
What to run at each pipeline stage (secrets, SAST, SBOM, image, IaC, admission, DAST, runtime), what should block, and a minimal workflow.
How attackers steal credentials from a CI/CD runner, and how to shut them out with OIDC, SHA pinning and admission-time verification.
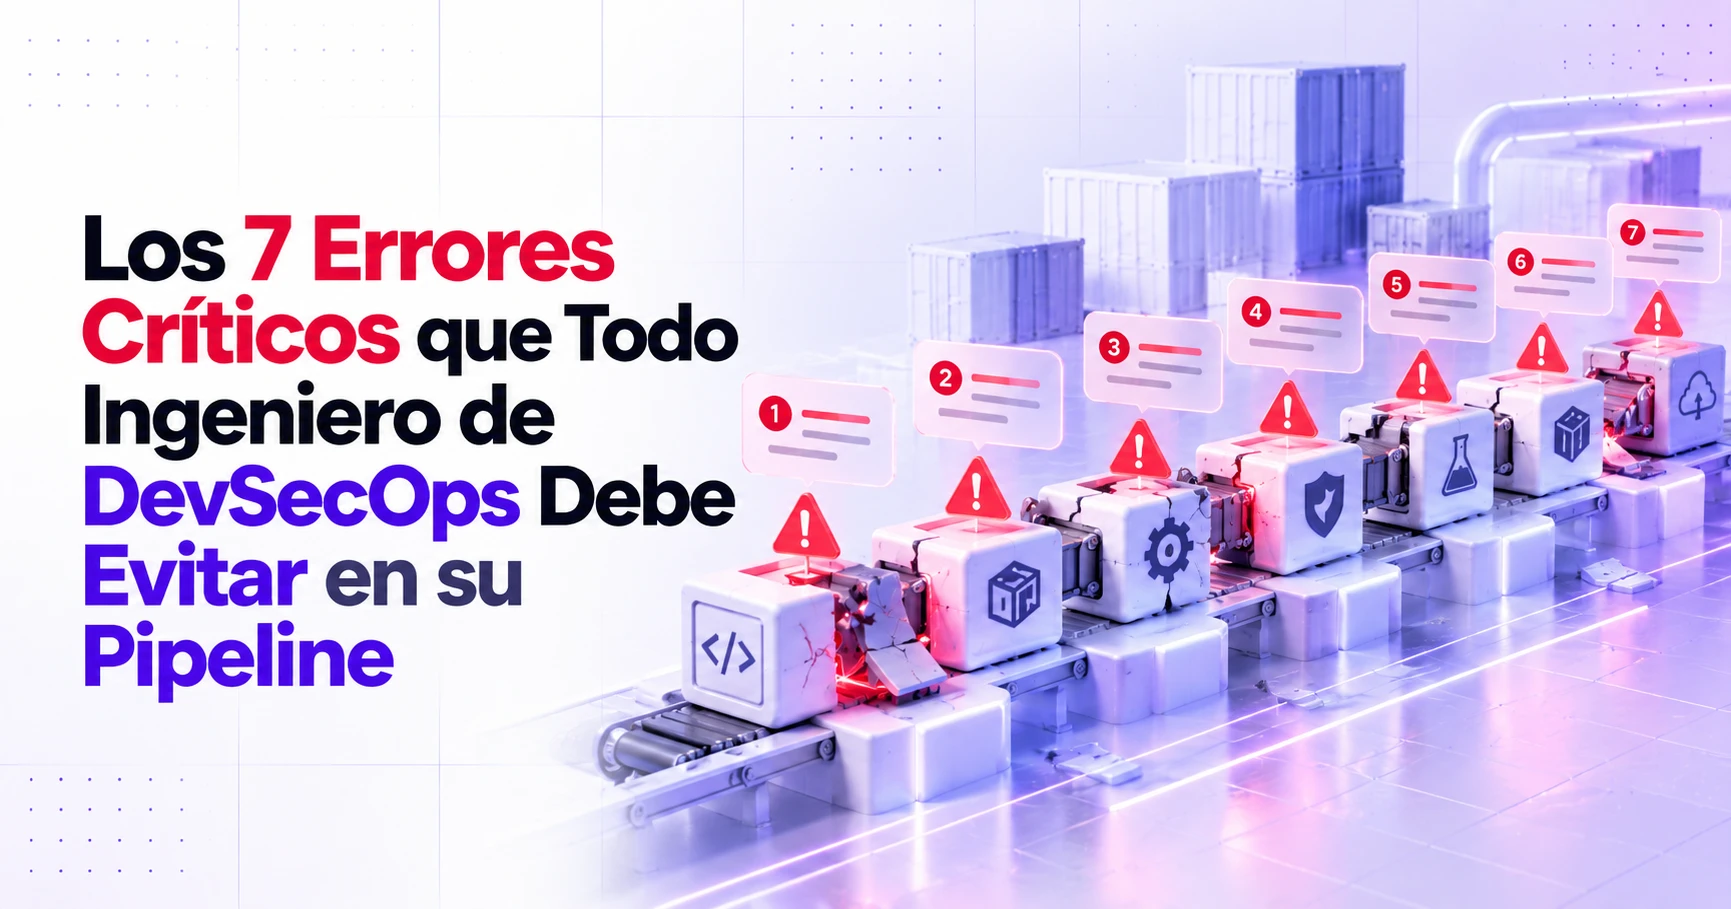
Seven pipeline mistakes and their fixes: Semgrep on the PR, a Snyk gate, CVSS with EPSS and KEV, pinned Actions, gitleaks, OIDC and ZAP in staging.
Complete implementation guide for zero-trust security in CI/CD pipelines. Learn to integrate security gates, RBAC, and supply chain attestation with GitHub Actions, GitLab CI, and Azure DevOps for enterprise-grade security automation.